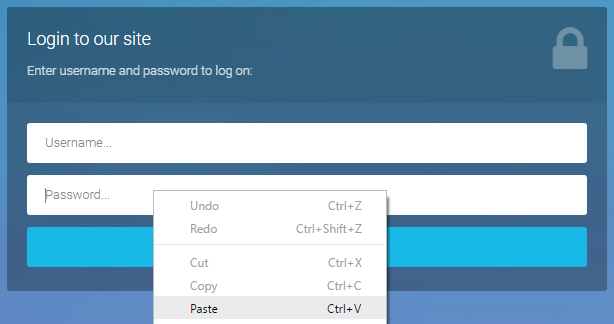
2fa Don't let them paste passwords... After months of tweets, emails & articles from eminent figures like Troy Hunt & the NCSC, it's about time I weighed in on the debate surrounding sites which disable a user's ability to paste passwords. The general consensus amongst many experts, including those mentioned above, is that disabling paste on password fields reduces security; the NCSC went one step further, calling it "completely pointless" and "damaging". So without further ado, allow me to explain why I believe disabling pas
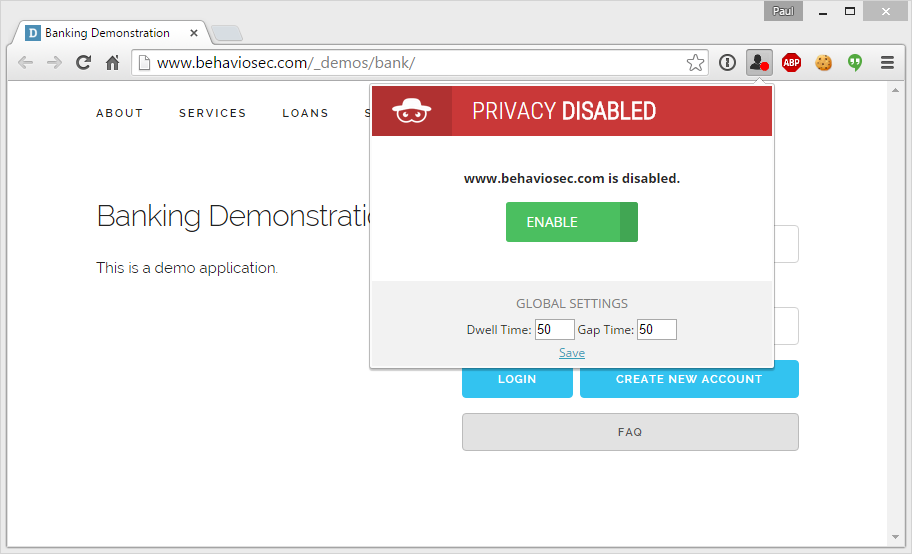
privacy Behavioral Profiling: The password you can't change. We're all familiar with the 3 basic categories of authentication. 1. Knowledge factors (passwords, PINs) 2. Possession factors (a software/hardware token - Yubikey/Google Authenticator/SecureID) 3. Inherence factors (fingerprint, heartbeat, iris/retina scanning) While the vast majority of sites use knowledge factors, a growing number are turning to multi-factor solutions in an effort to bolster security; to the detriment of the user experience. Cue continuous authentication / behavioral