privacy
PwnPhone: Default passwords allow covert surveillance.
A few weeks ago, I was asked to observe an installation of several wireless access points & VoIP phones, with a view to making recommendations on how best to improve security while maintaining ease of deployment. It didn't take long for several trends to appear; chief amongst which was the use of We'll just use defaults, for now. That password will do, for now. Of course, as soon as the device burst into life, it's on to the next one. At which point, "now" becomes a distant memory, alo
Privacy & Password Managers: A Reality Check
Before we begin, let me preface this by saying... I actually quite like Steve Gibson. For all his faults, he often raises very salient points on a variety of topics, typically surrounding security products & services. During the latest "Security Now / TWiT" episode on 20/10/2015, Steve & Leo Laporte featured a piece of 1Password news regarding Dale Myer's "1Password leaks your data" article. It's a little over 10 minutes long... It's no secret that Steve's a huge fan of LastPass and fo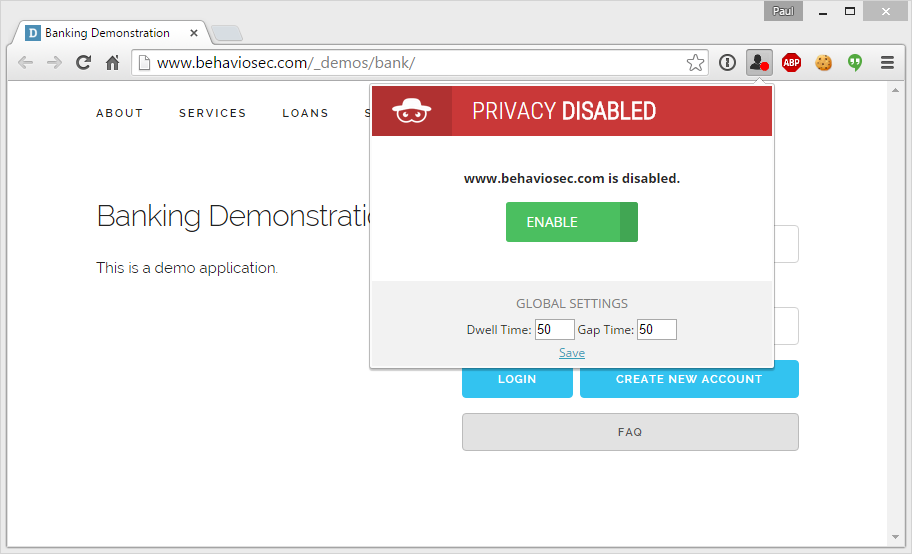
Behavioral Profiling: The password you can't change.
We're all familiar with the 3 basic categories of authentication. 1. Knowledge factors (passwords, PINs) 2. Possession factors (a software/hardware token - Yubikey/Google Authenticator/SecureID) 3. Inherence factors (fingerprint, heartbeat, iris/retina scanning) While the vast majority of sites use knowledge factors, a growing number are turning to multi-factor solutions in an effort to bolster security; to the detriment of the user experience. Cue continuous authentication / behavioral