Paul Moore
The shocking state of ZPos: Order takeaway & pay what you like.
In July 2020, I ordered a takeaway from Napolis Pizza. Like many firms across the UK, they use ZPos for their websites and electronic point of sale. A snazzy website, simple & easy to use ordering and minimal processing fees (compared to others in this space), it seems like a great deal for businesses and consumers alike. However, it quickly became clear that far from the "super secure" service they promote, it's an absolute mess which only places their client - and subsequently you & I - at c
Passwords: Using 3 Random Words Is A Really Bad Idea!
In 2015, the UK government released an article advocating the use of 3 random words in passwords, citing "pragmatism and algorithmic strength against common issues like brute force attacks". #Thinkrandom when creating passwords – #use3randomwords to make them https://t.co/6BlS8EqK7v pic.twitter.com/qtA43ffLf6 — Cyber Aware (@cyberawaregov) April 21, 2017 2 years later and a plethora of respected Twitter users continue to push this advice. If you're one of them (looking at you @WMPDigitalPCS
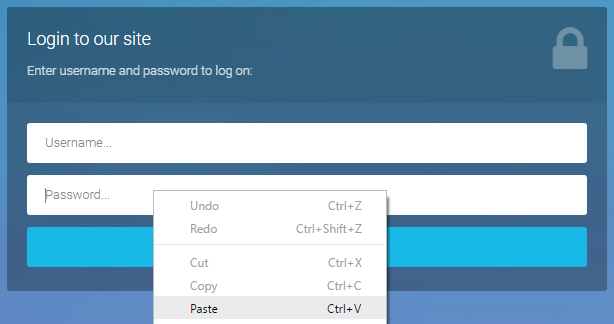
Don't let them paste passwords...
After months of tweets, emails & articles from eminent figures like Troy Hunt & the NCSC, it's about time I weighed in on the debate surrounding sites which disable a user's ability to paste passwords. The general consensus amongst many experts, including those mentioned above, is that disabling paste on password fields reduces security; the NCSC went one step further, calling it "completely pointless" and "damaging". So without further ado, allow me to explain why I believe disabling pas