passwords
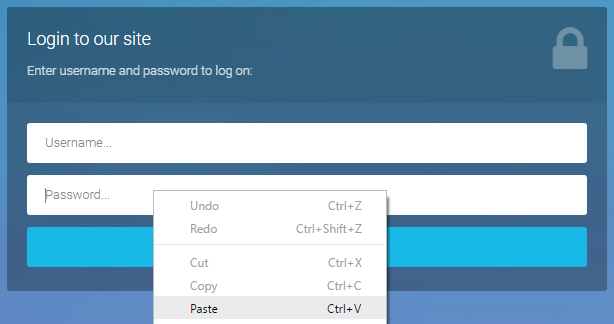
Don't let them paste passwords...
After months of tweets, emails & articles from eminent figures like Troy Hunt & the NCSC, it's about time I weighed in on the debate surrounding sites which disable a user's ability to paste passwords. The general consensus amongst many experts, including those mentioned above, is that disabling paste on password fields reduces security; the NCSC went one step further, calling it "completely pointless" and "damaging". So without further ado, allow me to explain why I believe disabling pas
PwnPhone: Default passwords allow covert surveillance.
A few weeks ago, I was asked to observe an installation of several wireless access points & VoIP phones, with a view to making recommendations on how best to improve security while maintaining ease of deployment. It didn't take long for several trends to appear; chief amongst which was the use of We'll just use defaults, for now. That password will do, for now. Of course, as soon as the device burst into life, it's on to the next one. At which point, "now" becomes a distant memory, alo
Roboform Security Revisited: Lies, Deception & Misnomers.
You may recall, I recently published an article entitled "How secure is Roboform: The 5 Minute Challenge". Well, 6 months have passed and although there's been no official public response from Siber Systems, they have made a number of comments to journalists and customers by email/Facebook and support tickets; during which I've been labelled as "misinformed", "unpleasant" and "sarcastic". There were no bugs in the first place. Roboform on Facebook Hmm. They edited the post.