security
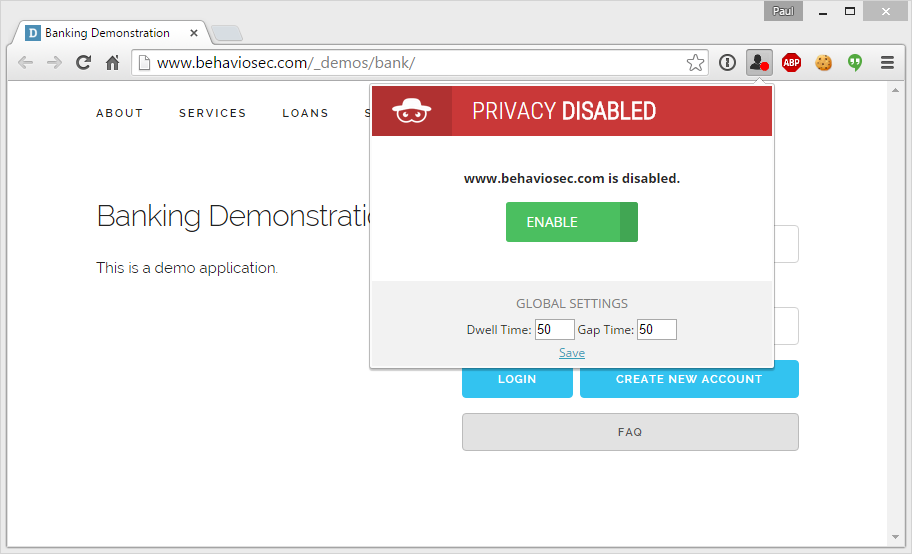
Behavioral Profiling: The password you can't change.
We're all familiar with the 3 basic categories of authentication. 1. Knowledge factors (passwords, PINs) 2. Possession factors (a software/hardware token - Yubikey/Google Authenticator/SecureID) 3. Inherence factors (fingerprint, heartbeat, iris/retina scanning) While the vast majority of sites use knowledge factors, a growing number are turning to multi-factor solutions in an effort to bolster security; to the detriment of the user experience. Cue continuous authentication / behavioral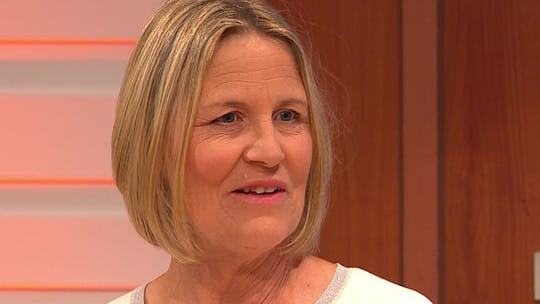
Phishing attacks are evolving. The Vivian Gabb story...
"We have detect some unauthorized active on your account. Please update your detail as soon as possible" We've all had them; the notorious and grammatically inept phishing emails designed to strip us of our hard-earned money. The vast majority are destined for immediate deletion, but a growing number of sophisticated attacks are starting to emerge. Nobody understands this better than Vivian Gabb, a tennis coach from London who recently lost nearly £50,000 to fraudsters. Before you cast
Everykey: 3 years and $250,000... is it vaporware?
Update 22/12/2015 I've received several emails regarding this project over the last few months; another landing just a few moments ago. Unbelievably, Everykey has been delayed yet further... with delivery now estimated in February 2016. I'm very grateful to everyone for keeping me informed. However at this stage, there's not a great deal I can add to the discussions. It's a great idea with (I believe) real potential... but talk of "receiving samples" after 3 years and $1.2 million dollars
Roboform Security Revisited: Lies, Deception & Misnomers.
You may recall, I recently published an article entitled "How secure is Roboform: The 5 Minute Challenge". Well, 6 months have passed and although there's been no official public response from Siber Systems, they have made a number of comments to journalists and customers by email/Facebook and support tickets; during which I've been labelled as "misinformed", "unpleasant" and "sarcastic". There were no bugs in the first place. Roboform on Facebook Hmm. They edited the post.
Immobilise: Police Security Initiative Exposes 28 Million Records.
05/01/2015: Recipero, the company behind Immobilise, NMPR and CheckMEND have now mitigated this risk by limiting access to the "/verify" & pdf generation pages to only authorized users. You're no longer able to view records which you do not own, so although it's undoubtedly more secure, the inability to verify the authenticity of a certificate appears to render this process pointless. This exploit is known as a direct object reference, though I colloquially refer to it as the "open DOR" at
Password Managers: Facts, Fallacies & FUD
Ah, passwords. The thought of choosing, remembering and inevitably resetting them is enough to make your blood boil. As a fundamental part of our digital lives and despite several reports claiming they're dead, our dependence on them shows little sign of slowing. A password manager is a great way to virtually eliminate the stress & hassle associated with passwords; itself sufficient reason to give them a whirl. Pick a good one though, and you'll almost certainly be safer too. What do t
Kickstarter Password Managers: The good, the iffy and the dangerous.
Over the last few months, Kickstarter has been awash with password managers. Unless you're willing to invest and use a ridiculously tiny comments box, it's impossible to comment or ask further questions so others can see their response. Rather than clutter the comments area, this article will provide a very high-level overview of each product; a summary of why you should/shouldn't use them. Don't forget to bookmark it, as it's likely to be updated frequently. Kickstarter: https://www.ki